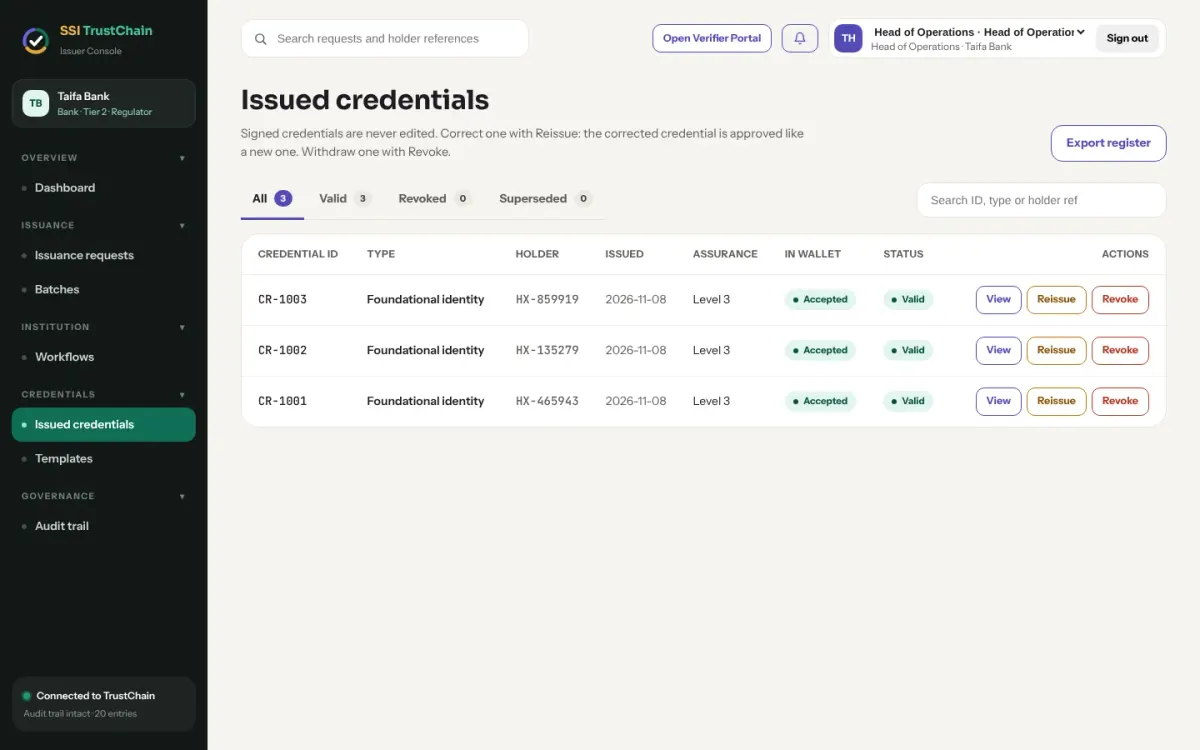
Every credential you signed
Issued, accepted into wallets, valid or revoked. Correct one with Reissue, withdraw one with Revoke and a reason: never an edit.
Issuer ConsoleSSI TrustChain
For universities, colleges, schools, hospitals, councils, banks and identity partners. Keep your own sealed records, design certificates, set approval paths, and sign credentials that people carry in their wallets for life.
What it does
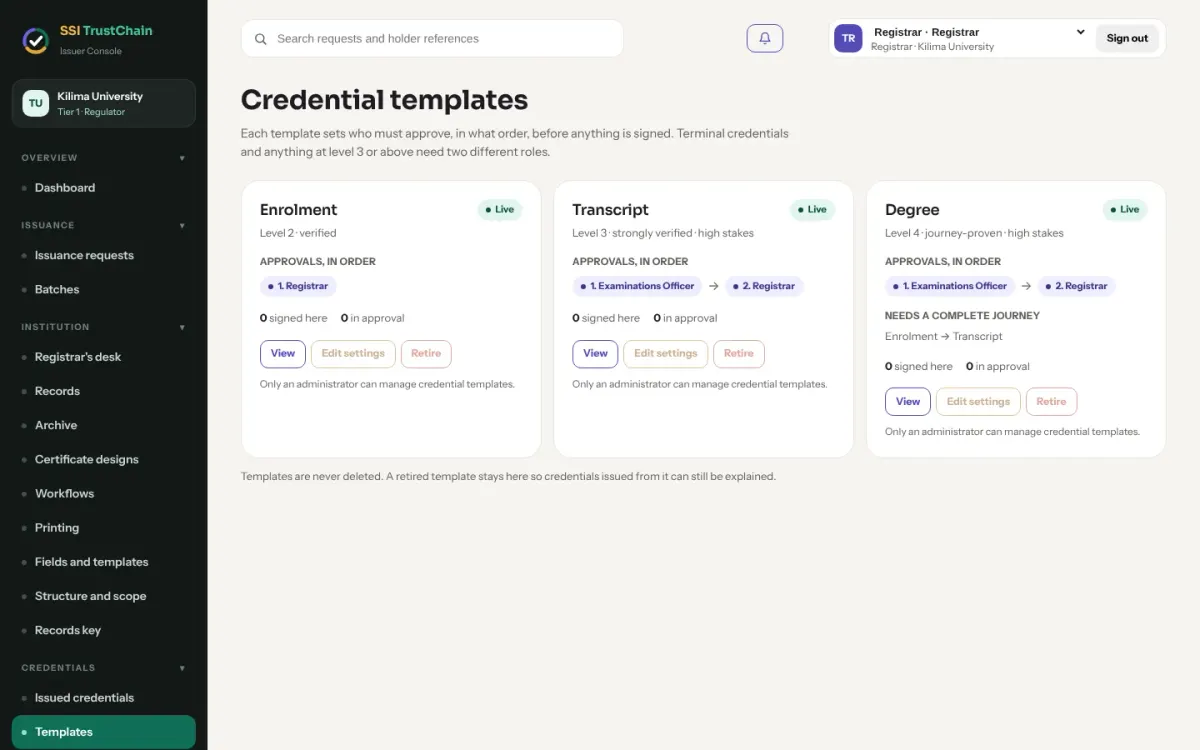
Each credential type has a path to signing: a senate or board vote, approvals by the right roles in the right units, then a signature. Nobody approves their own draft, and high-stakes types need two different roles.
Student and staff records are encrypted in your staff browsers to your institution's own key, unit by unit. TrustChain keeps ciphertext; every opening is in your audit trail.
A degree is signed only over a complete, in-order and unrevoked chain: admission, each year's transcript, then the award. A forged certificate cannot fake four years of signed history.
Design your certificates (branding, wording, signatories, security profile), approved by a second person. Every credential comes with a PDF and a check code; print on your own numbered paper with spoilage and hand-over tracked.
Upload a cohort, have approvers spot-check a sample with personal details masked, then sign. Rows are sealed at rest and deleted when the batch ends.
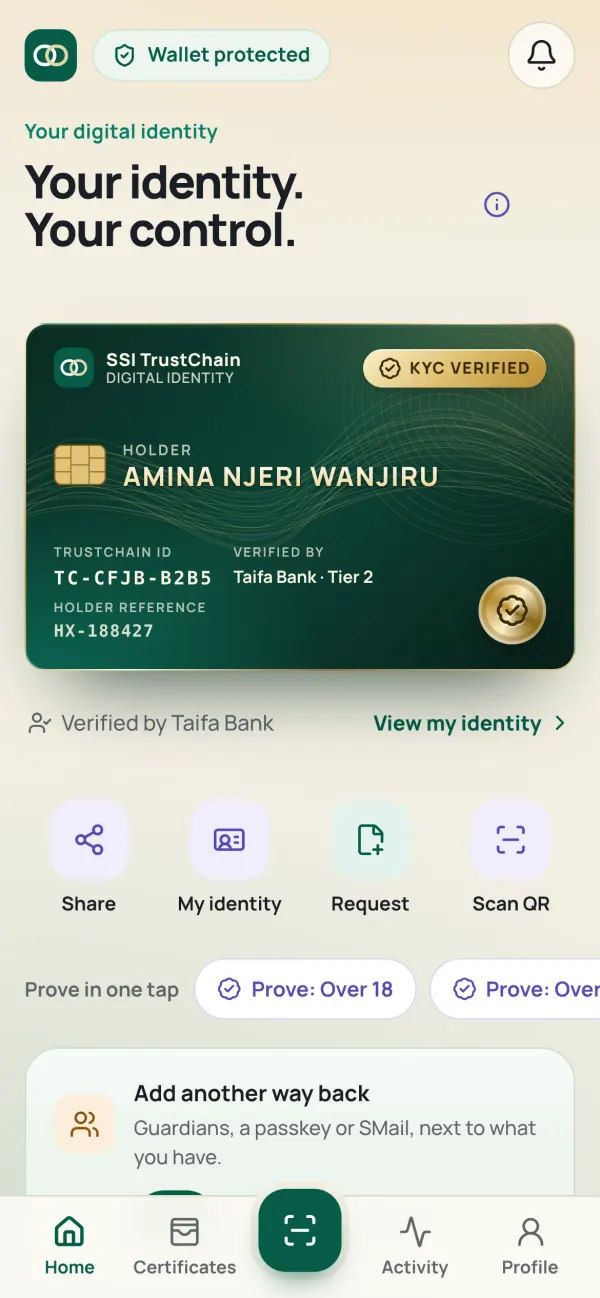
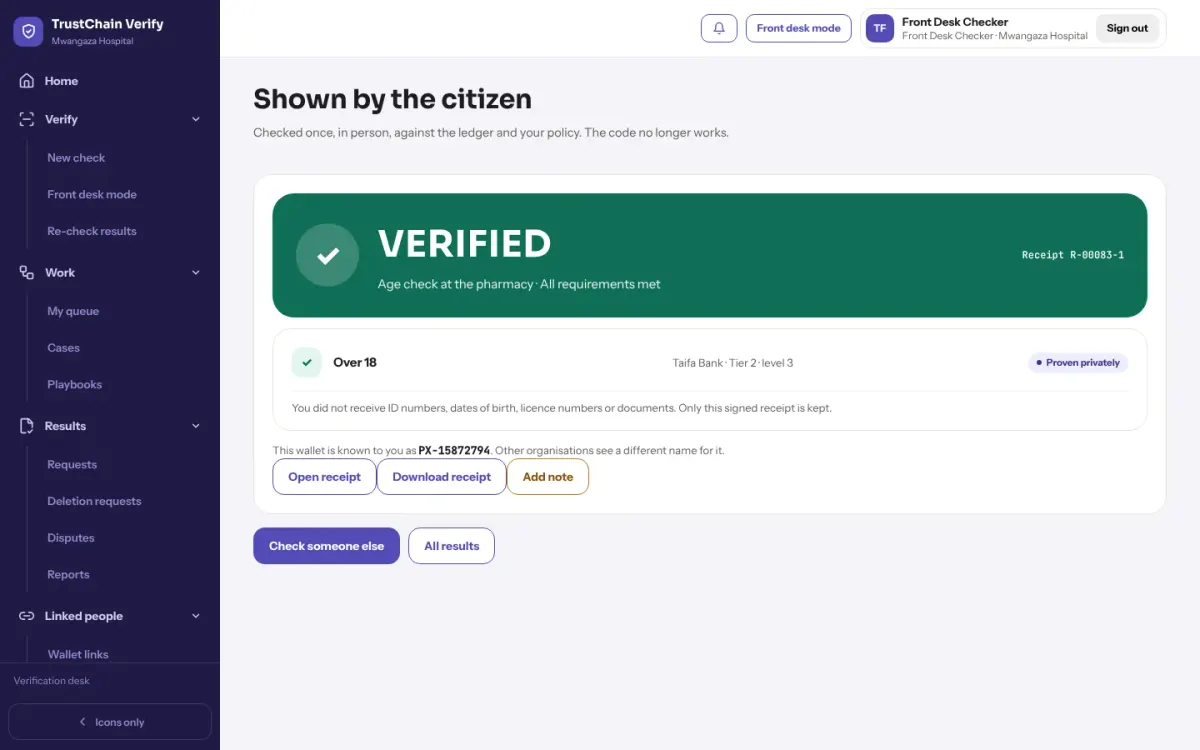
Each credential goes to a wallet whose identity was verified in person, matched through the identity index and never stored. Mismatches pause, person by person.
Your signing key is created in AWS KMS (with HSM standby keys) and never leaves it. Revocations publish to a public status list at once.
Your student or HR system drafts credentials over /api/v1 with OAuth client credentials, idempotent writes and signed webhooks. People always approve and sign.
See it
Real screens from the app, with invented sample names and figures.
Issued, accepted into wallets, valid or revoked. Correct one with Reissue, withdraw one with Revoke and a reason: never an edit.
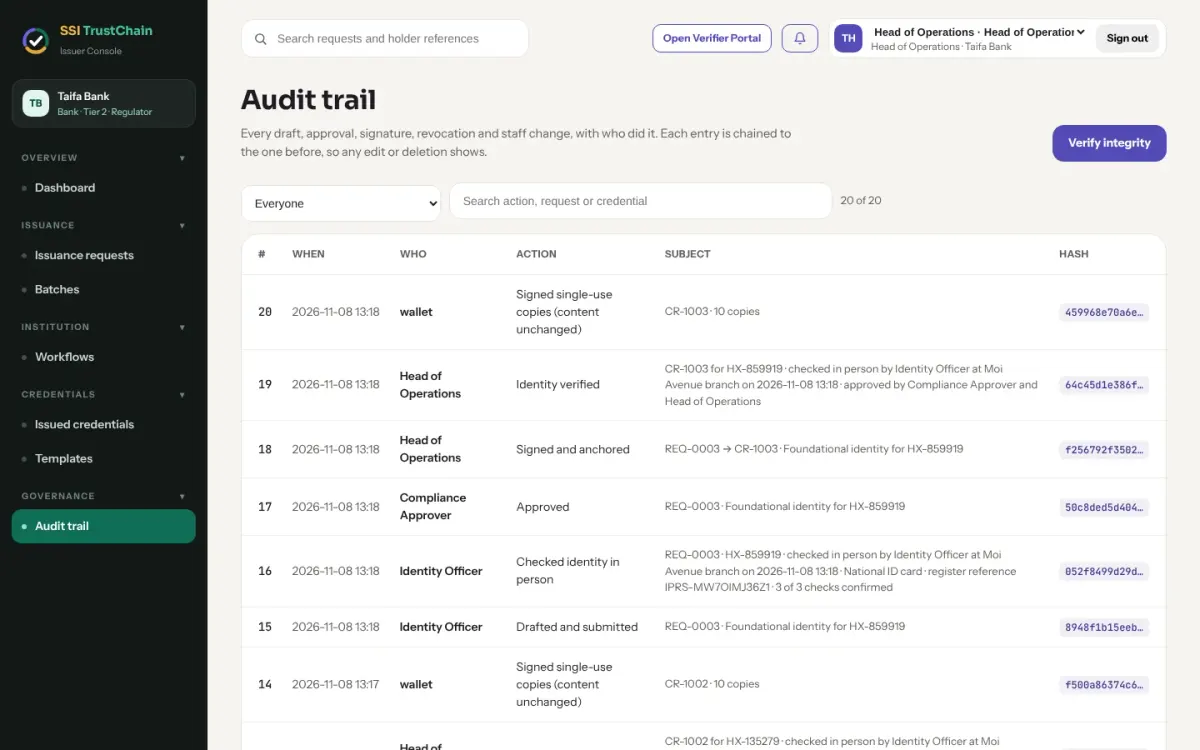
Every draft, approval, signature and revocation, with who did it, chained by hash and checkable by your auditors.
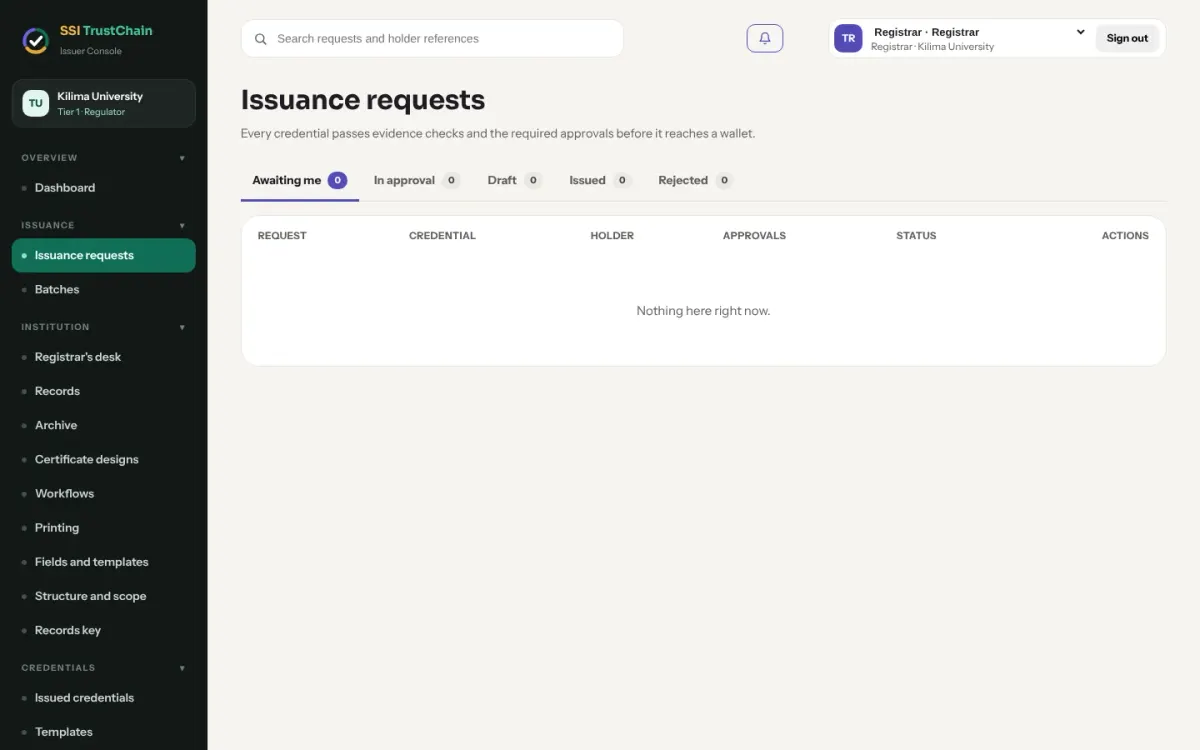
Drafts, approvals in order and signatures, with nobody approving their own draft.
How the trust works
An officer drafts from your records; the holder is a pseudonymous reference.
The path you set: votes, approvals by role and unit, each audited.
Signed with your institution's key in secure hardware; its fingerprint goes on the ledger.
The credential, its SD-JWT VC copies and its PDF go to the wallet. Revoke or reissue later, never edit.
What you achieve
One identity
Sign in once with your verified wallet. What you seal in one app opens in the others, on every device you use.
Never edited. A mistake is corrected by a reissue that passes the whole approval path again; the old one is superseded only when the new one is signed. Or it is revoked with a reason.
Your own staff, for the units their role covers. They are sealed to your institution's key, held only in your staff browsers. TrustChain cannot open them.
Apply, pass vetting, and two TrustChain people accredit you. Your entry then appears in the public registry and your keys are created.
We are onboarding the first institutions and organisations. Tell us what you issue or check today.